Deliverables
Reports people actually read, not raw output
Branded, severity-ranked PDFs
Every scan becomes a report anyone can actually read — findings ranked by severity with plain-English remediation. Hand it to an auditor, a boss, or a client.
Nmap · Nuclei · ZAP · testssl.sh — one console, zero install
From $10 · Credits never expire
As featured in
Platform
Hosted Nmap, Nuclei, testssl.sh, and OWASP ZAP. Pick a target and hand over a branded, deliverable report in minutes.
Branded, severity-ranked PDFs
Every scan becomes a report anyone can actually read — findings ranked by severity with plain-English remediation. Hand it to an auditor, a boss, or a client.
Pay per scan, no annual contract
10 assessments from $10 — no $4k/yr Nessus seat or Qualys contract to spread across your budget.
We run the scanners, you pick targets
Hosted on tuned, continuously-updated servers. No appliances, no patching, no VM to babysit between scans.
One console, many targets
Scan and report for all your environments from one place. Onboard a new target in minutes instead of provisioning another tool.
Nmap + Nuclei + ZAP + testssl.sh
Four battle-tested engines security pros trust — open ports and services, template-based CVE detection, web-app DAST, and TLS auditing — across one workflow.
Not a day in a console
Kick off a scan and get a finished, deliverable report back in minutes — fast enough to run between meetings.
Scanners
Each engine is tuned, patched, and continuously updated on our side. You pick the target, we handle the rest.
Fast open-port & service discovery — identifies what's exposed, what's running, and what version on every target.

Template-based vulnerability detection mapped to current CVE intelligence and refreshed daily.

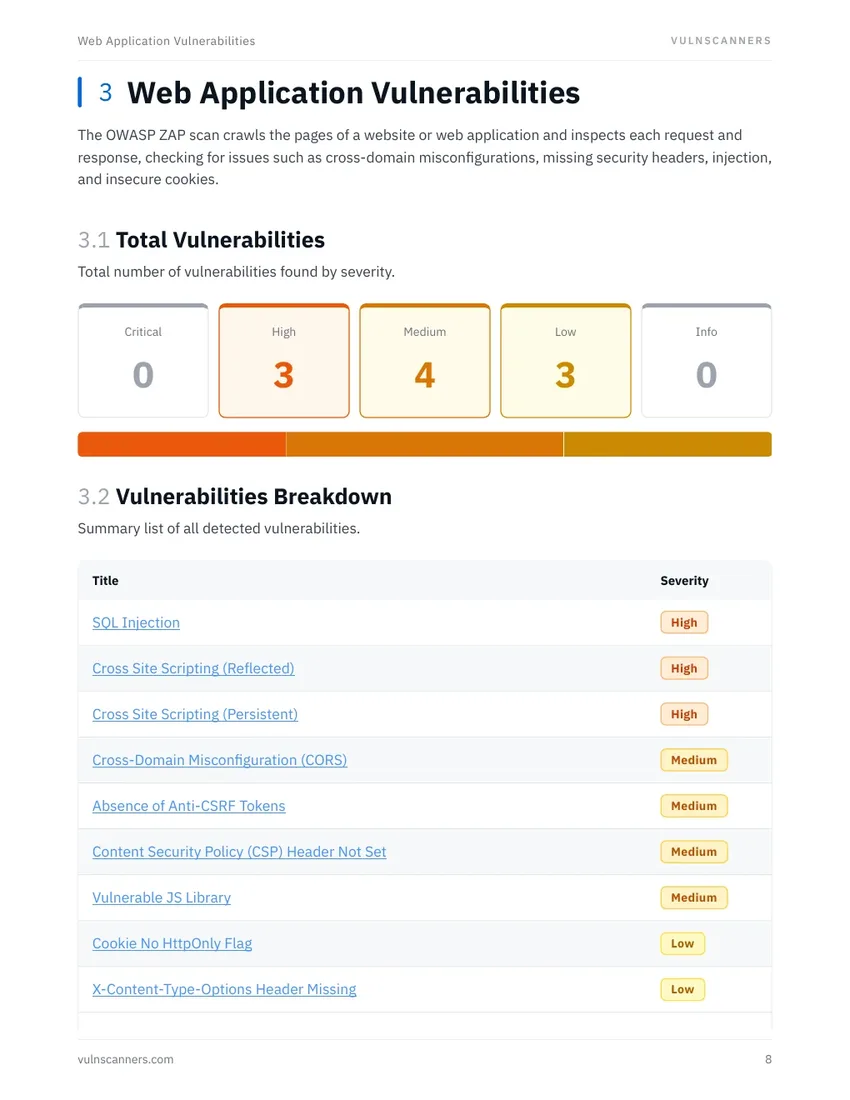
Automated web-layer security baseline — crawler, passive analysis, handoff-ready reports.
TLS/SSL configuration audit — protocol support, cipher strength, certificate chain, and known attacks.
The problem
Stop relying on clunky, self-hosted security software that demands dedicated servers, endless patching, and constant manual upkeep.
Licenses, servers, power, cooling and the engineer stuck babysitting scanner uptime — all add invisible, recurring costs.
Missed patches and stale feeds mean critical vulnerabilities go undetected until it's too late.
Security teams get pulled into infrastructure firefights instead of triaging and fixing real vulnerabilities.
What customers say
“Extremely reasonable pricing, very nice UX and very well laid out and comprehensive reports. Was impressed that it's setup by default to traverse the supplied URL. The best we have seen in this sector, by far.”
Key features
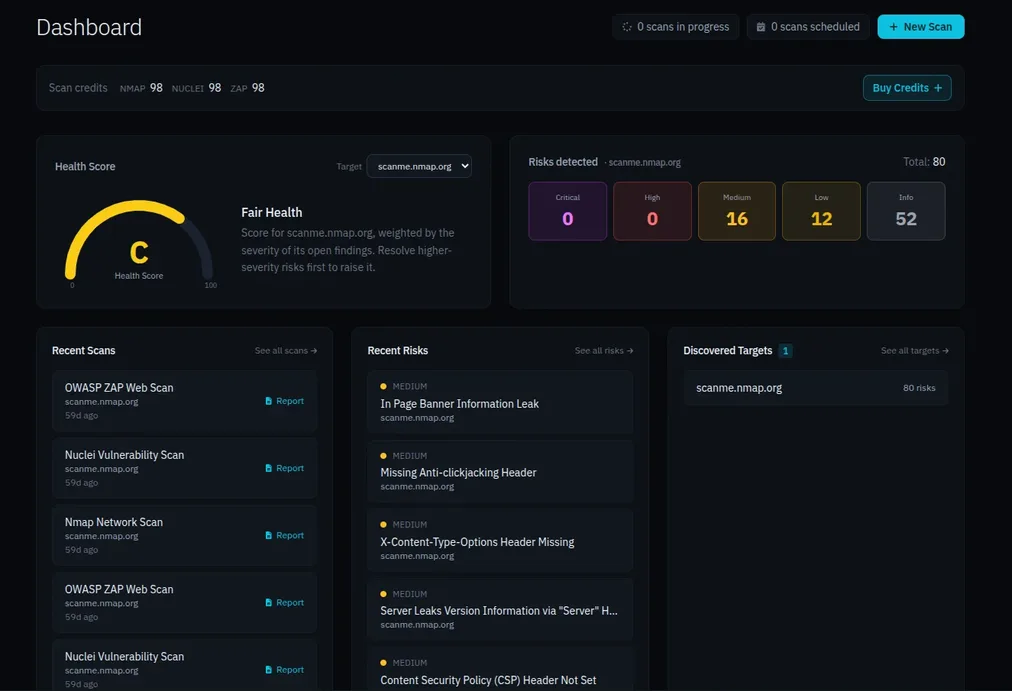
Identify forgotten assets and poorly maintained endpoints. Complete network visibility for both Red and Blue Teams.
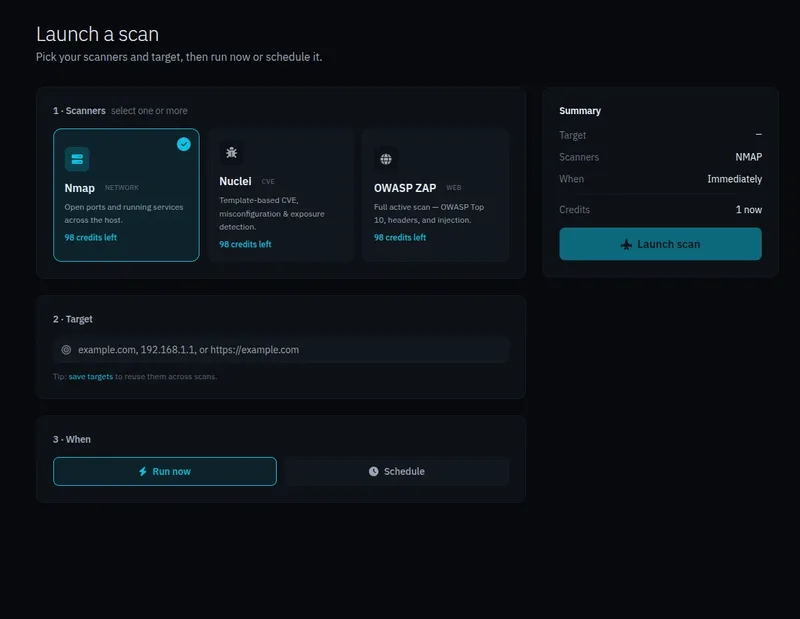
Fully hosted service with nothing to install or maintain. Launch scans whenever you need, from anywhere.
Nuclei and Nmap scans for ongoing vulnerability detection and firewall monitoring.
Launch comprehensive vulnerability scans with a simple form. Select your options and receive detailed results.
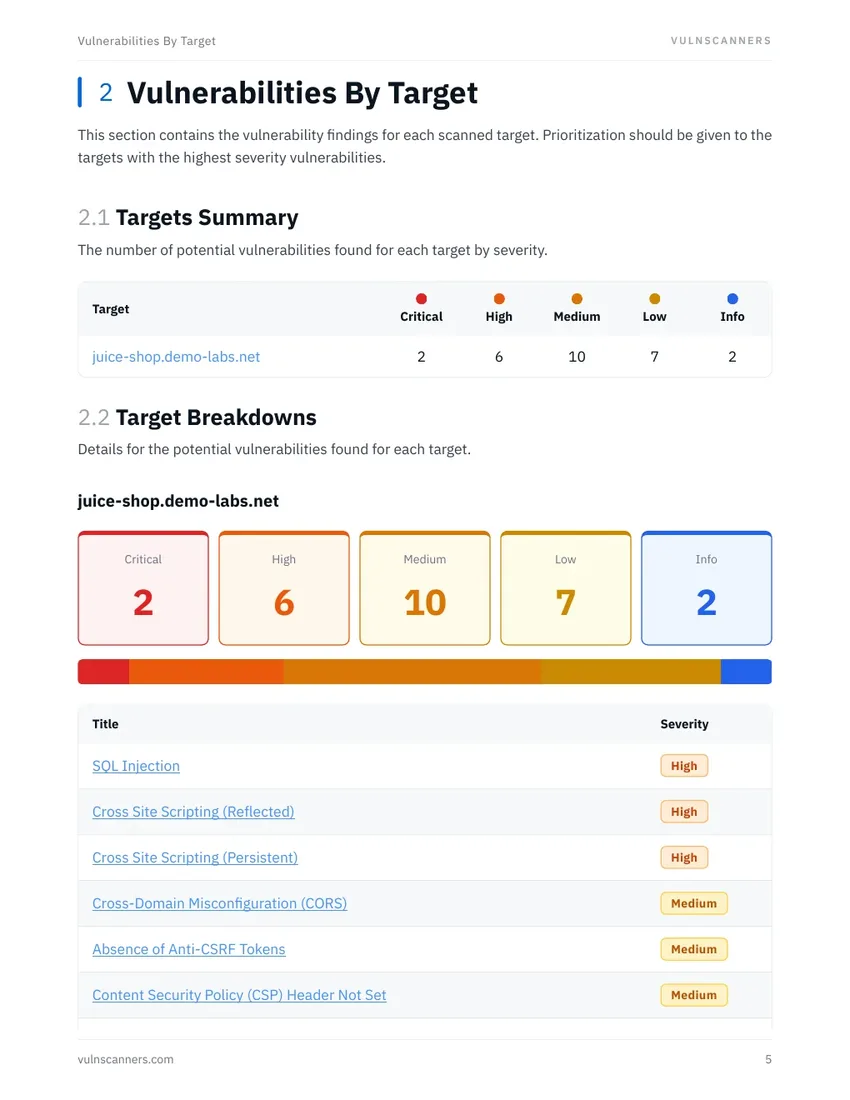
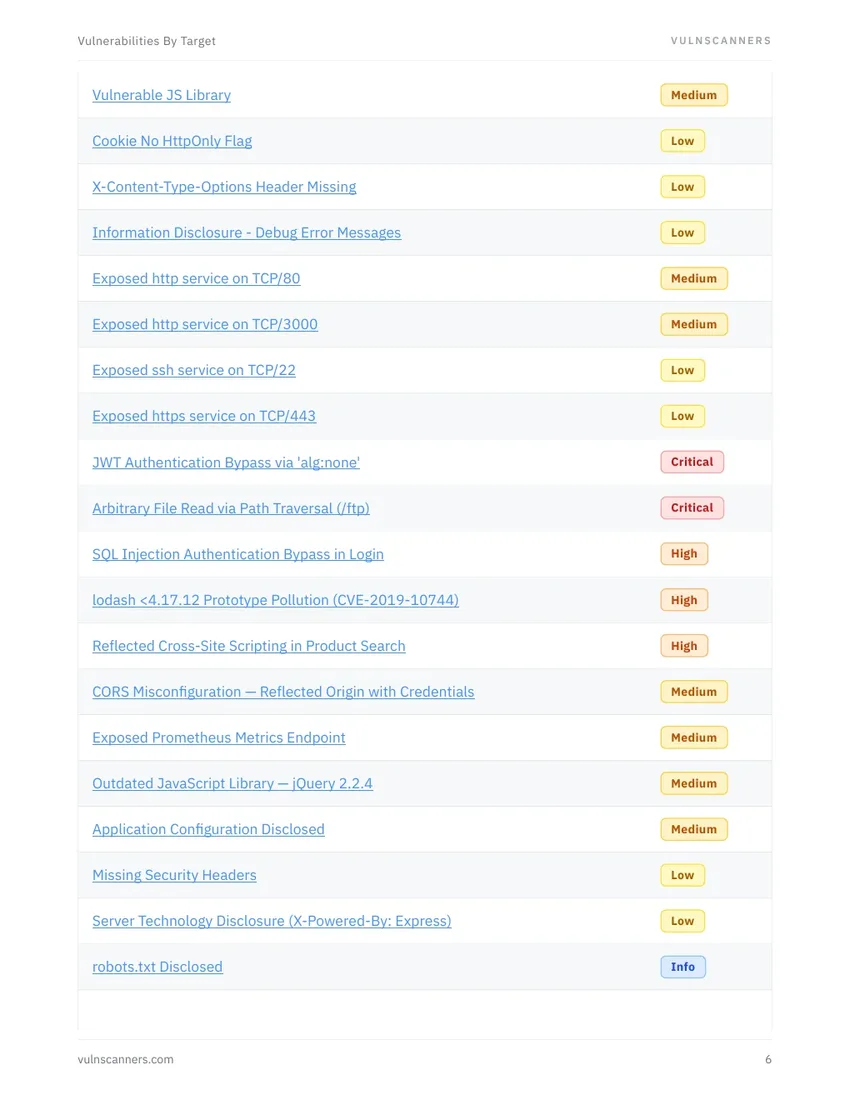
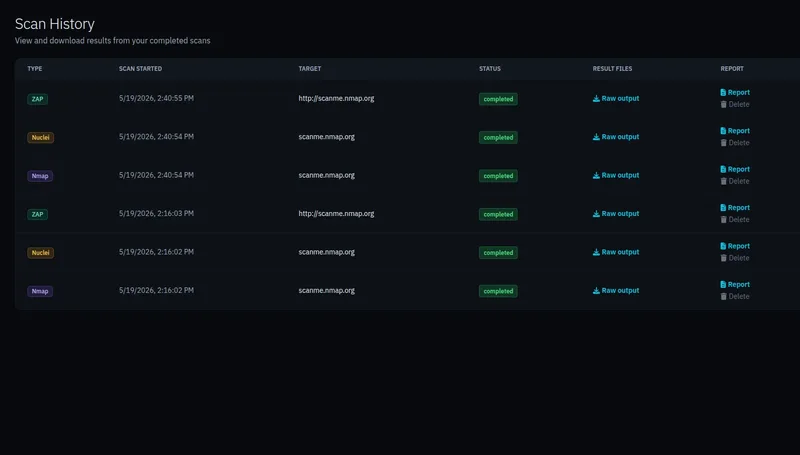
Every scan generates a branded, client-ready PDF report — share findings with clients, auditors, and stakeholders without extra work.
Compliance
The frameworks your customers and auditors hold you to already require exactly what VulnScanners automates.

“Continuously acquire, assess, and take action on new information in order to identify vulnerabilities, remediate, and minimize the window of opportunity for attackers.”

“Run internal and external network vulnerability scans at least quarterly and after any significant change in the network.”

“Monitor and scan for vulnerabilities in the system and hosted applications, and when new vulnerabilities potentially affecting the system are identified and reported.”

“Organizations that do not scan for vulnerabilities and address discovered flaws pro-actively face a significant likelihood of having their computer systems compromised.”
How we compare
The legacy scanners were built for enterprise security teams with servers to spare — not for delivering a clean report today.
| VulnScanners | Nessus | Qualys | Intruder | |
|---|---|---|---|---|
| Fully hosted — nothing to install | Agent / appliance | |||
| Nmap + Nuclei + ZAP + testssl.sh in one console | ||||
| Client-ready, branded PDF reports | Raw export | Raw export | ||
| Pay per assessment — or subscribe and save | ||||
| Billing model | 10 assessments from $10 | Annual license | Enterprise quote | Monthly subscription |
| Time to first report | Minutes | Hours | Days | ~Minutes |
| Built for MSP multi-client work | Limited | Limited | Limited |
Pricing
One assessment = a full Nmap + Nuclei + ZAP + testssl.sh pass on one target with a client-ready PDF report. Buy packs one at a time or subscribe — credits never expire either way. No seats, no overages.
MSP? We offer volume pricing for managed providers running our hosted scanners across multiple clients. Need something custom? Contact sales.
Request a meetingFor managed providers
Every report you ship is branded as yours, every audit gets its evidence, and every client you add costs you minutes — not another server to babysit.
ROI calculator
Value recovered every month
$897
Assumes ~3 hours saved per full assessment (Nmap + Nuclei + ZAP + TLS). 10 assessments from $10 (~$1 each), or ~$0.80 on the Pro 100 pack. Slide to your real numbers.
Put your own logo on the PDF. Your client sees your brand — a quiet "Powered by VulnScanners" is the only thing that points back to us.
Vulnerability scanning for MSPs →Refer another provider and earn scan credits or reseller margin. Your network becomes a channel.
MSP scanning program →Cyber-insurance, CMMC, SOC 2 and vendor questionnaires all expect continuous scanning. Hand auditors the evidence in one file.
See compliance coverageBegin with a $10 assessment for a single client, then move to the Agency plan as your book grows.
See pricingSee the deliverable
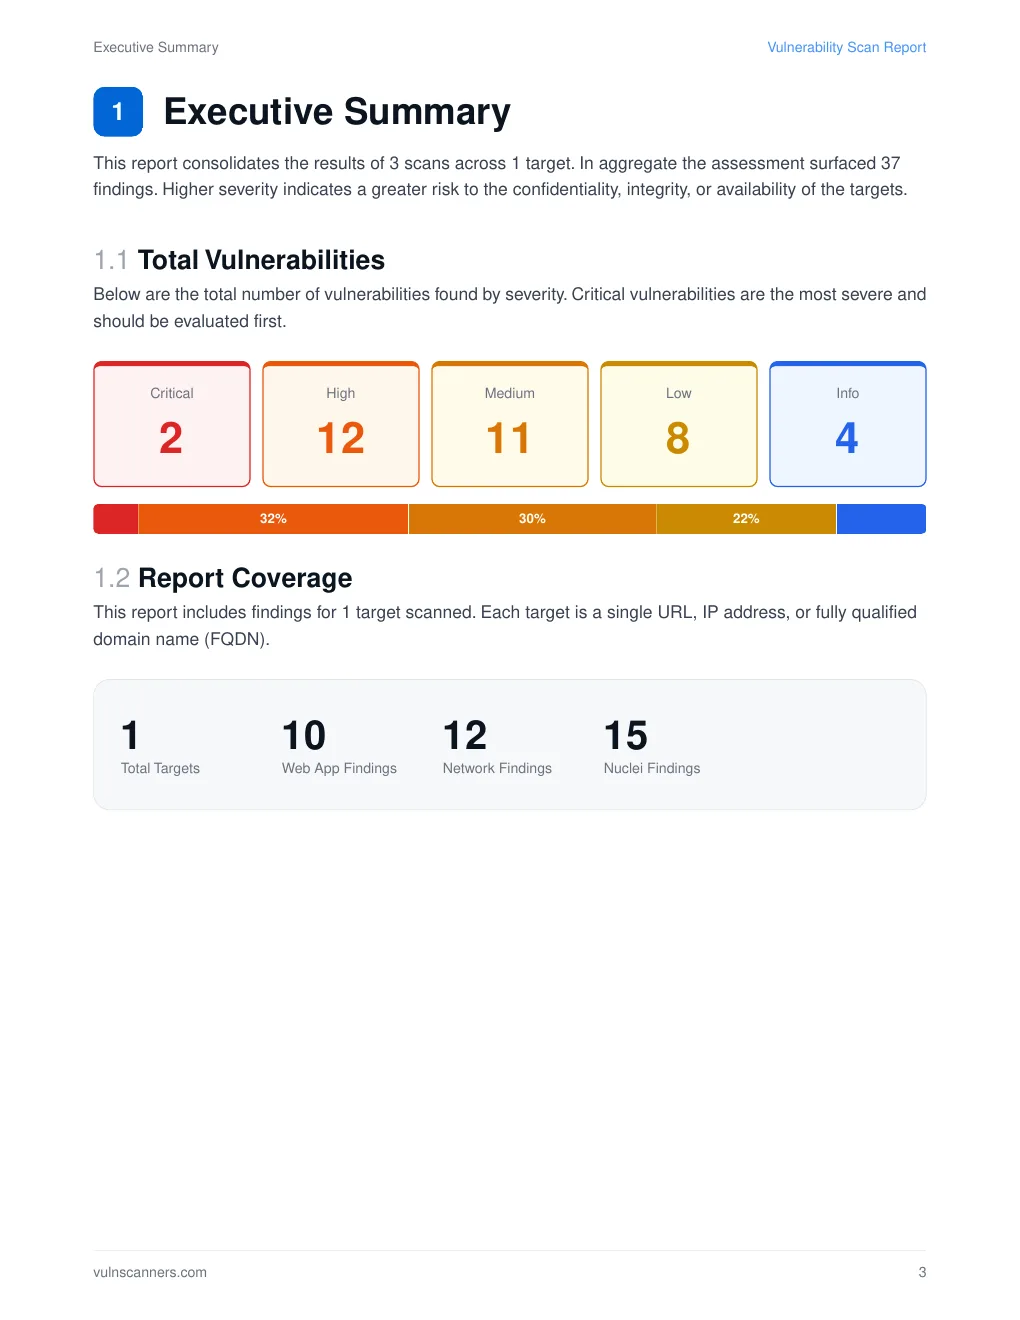
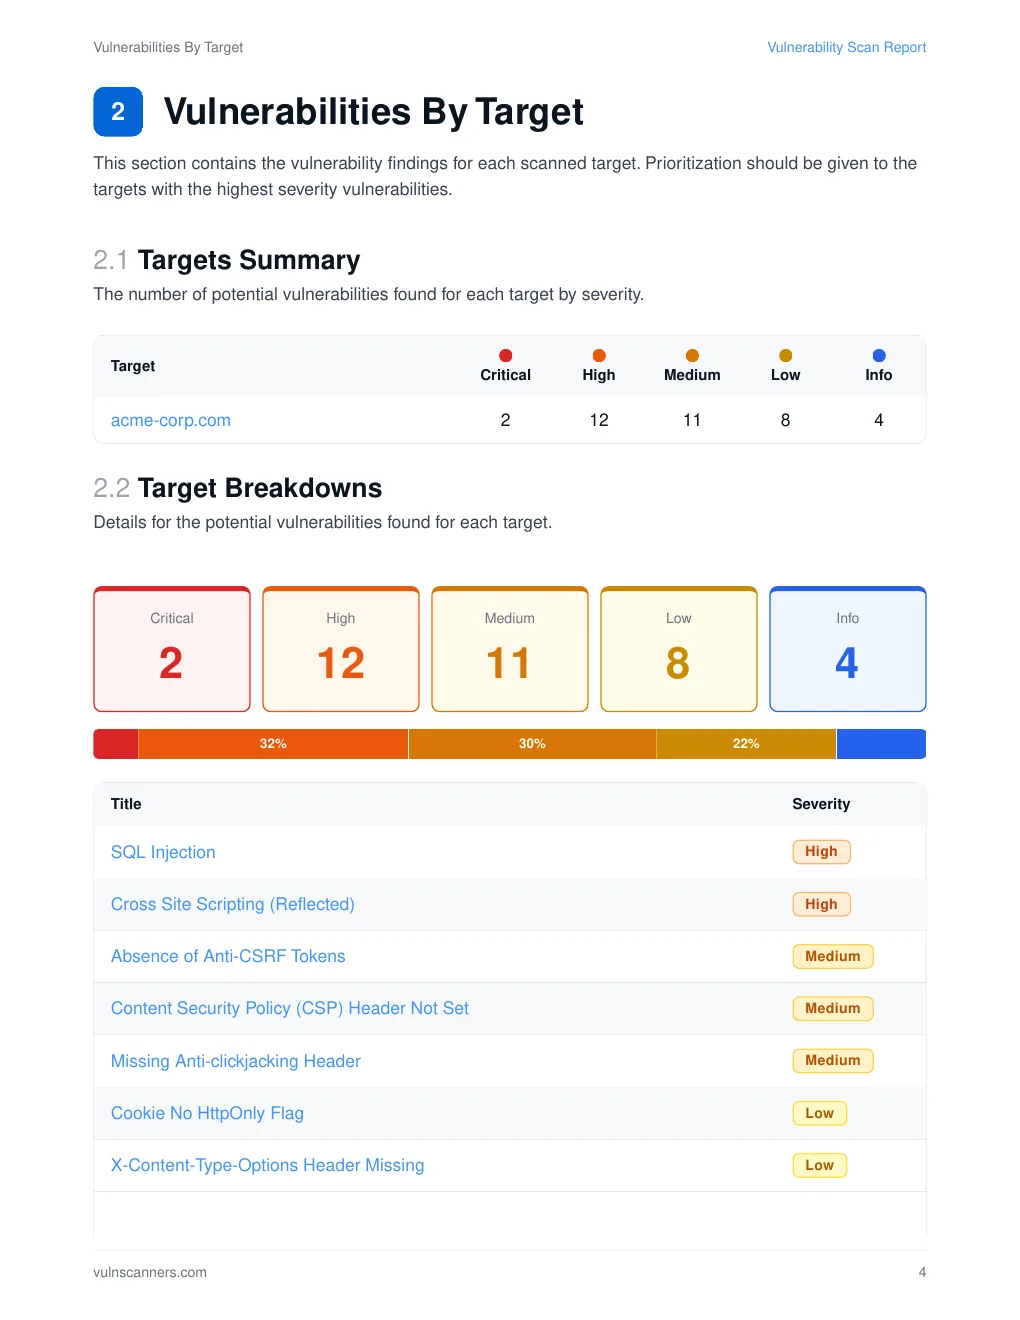
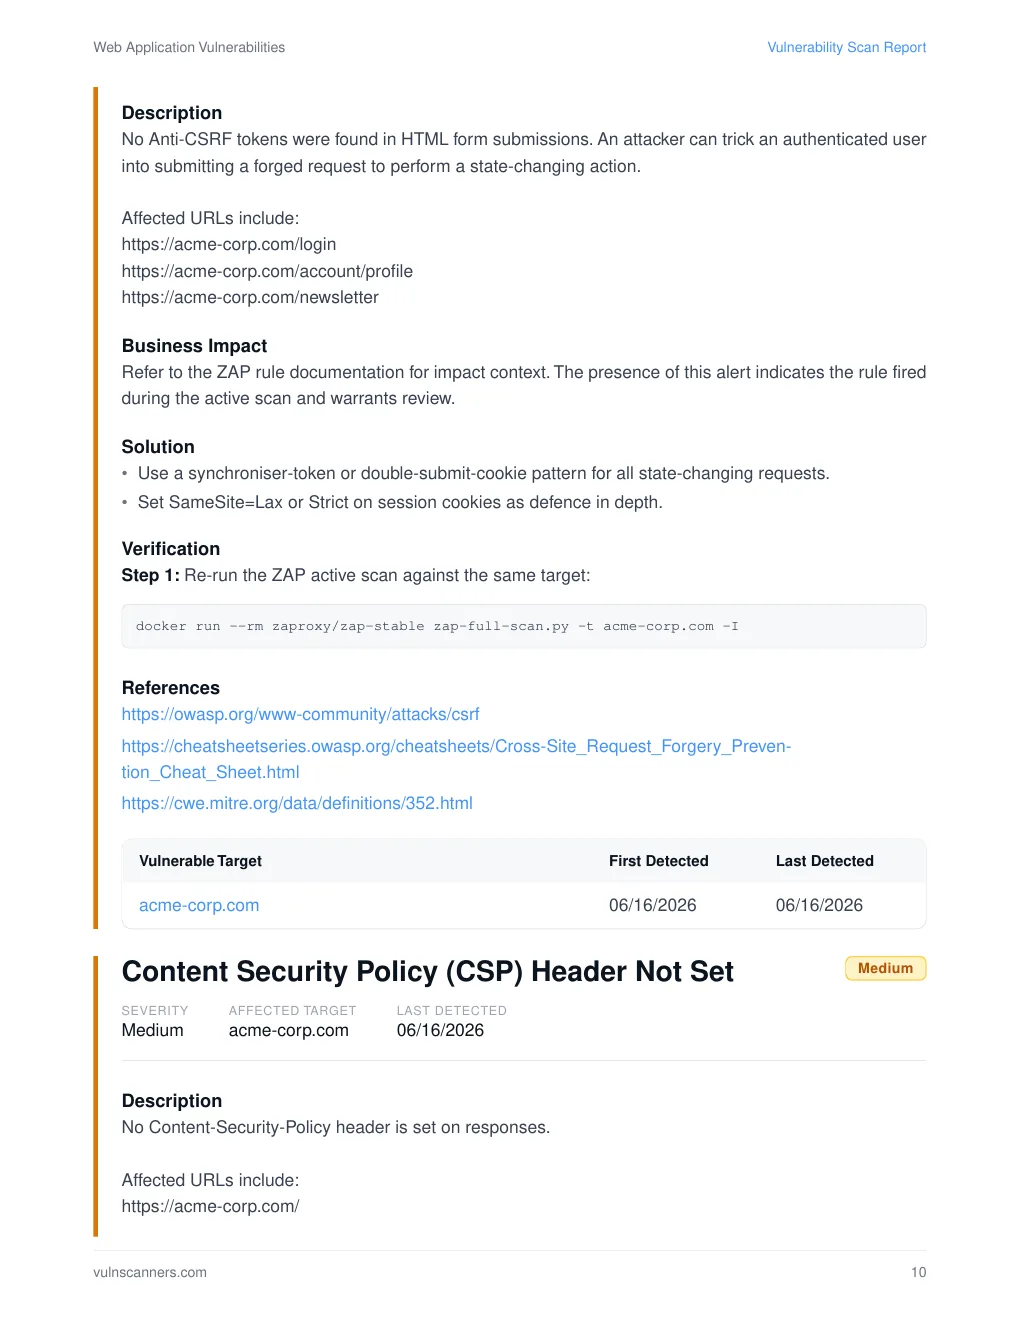
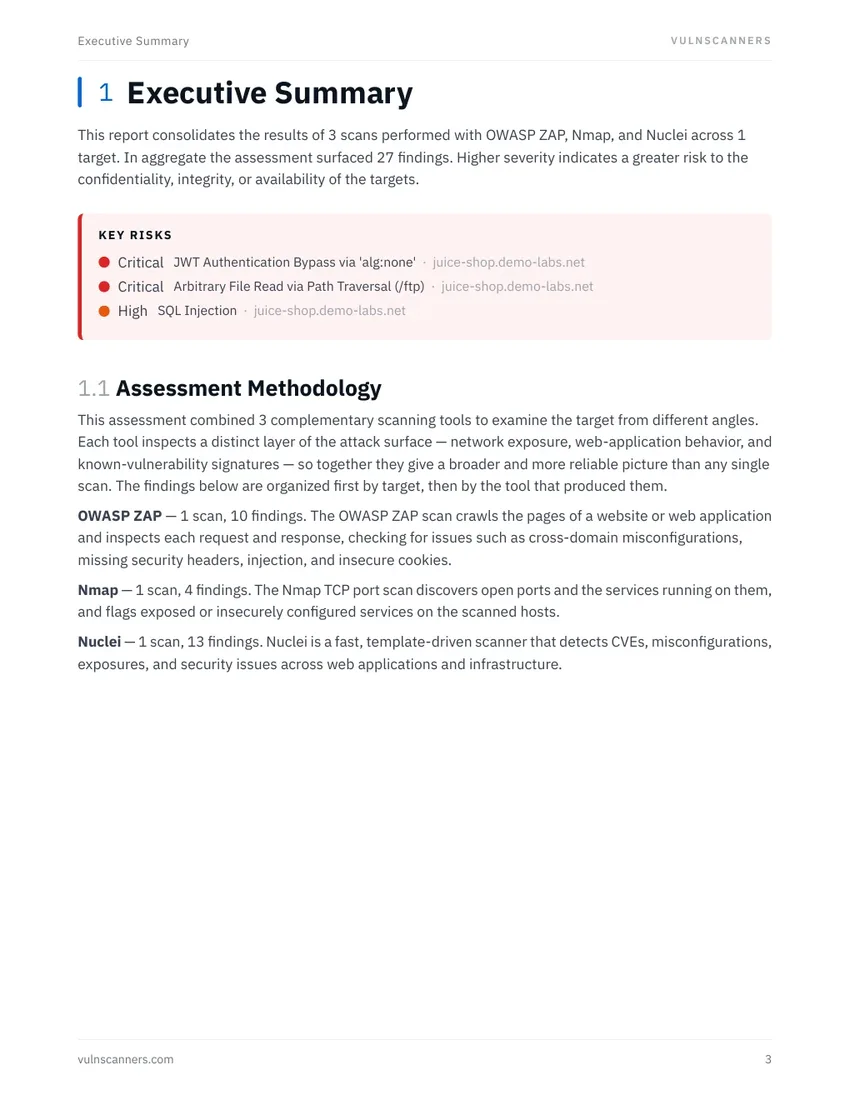
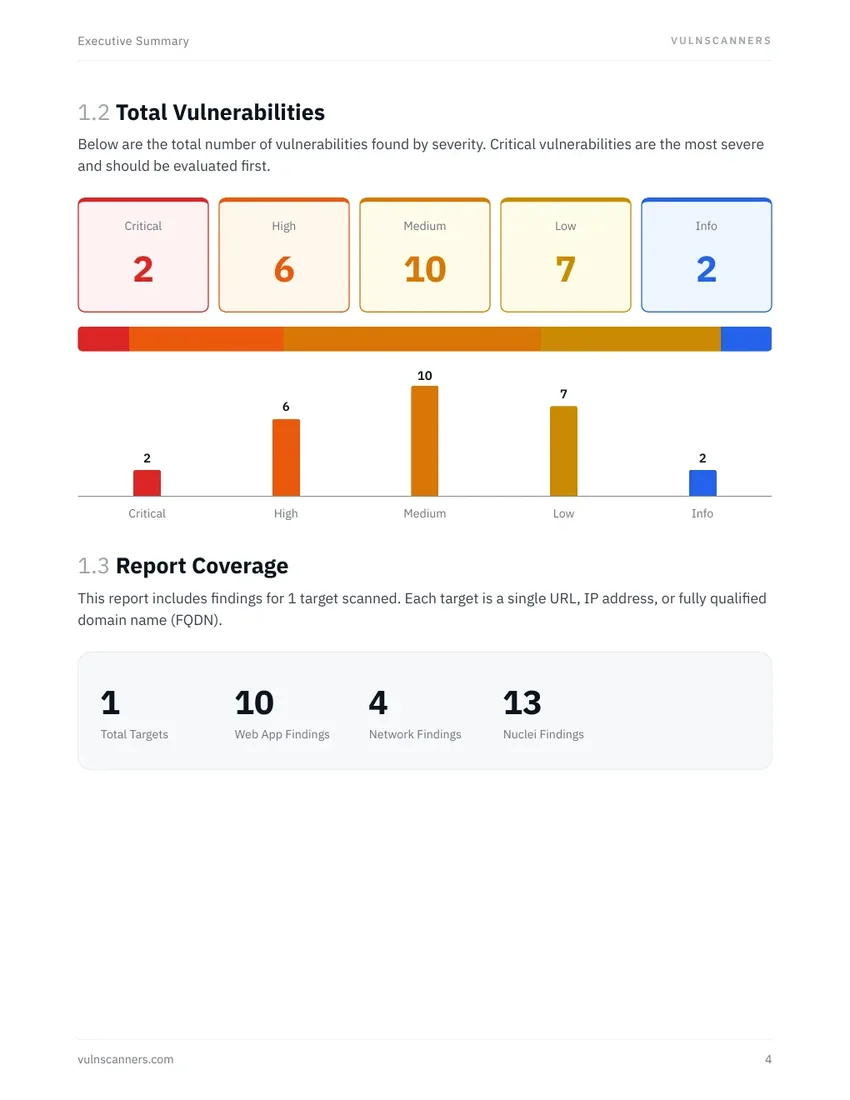
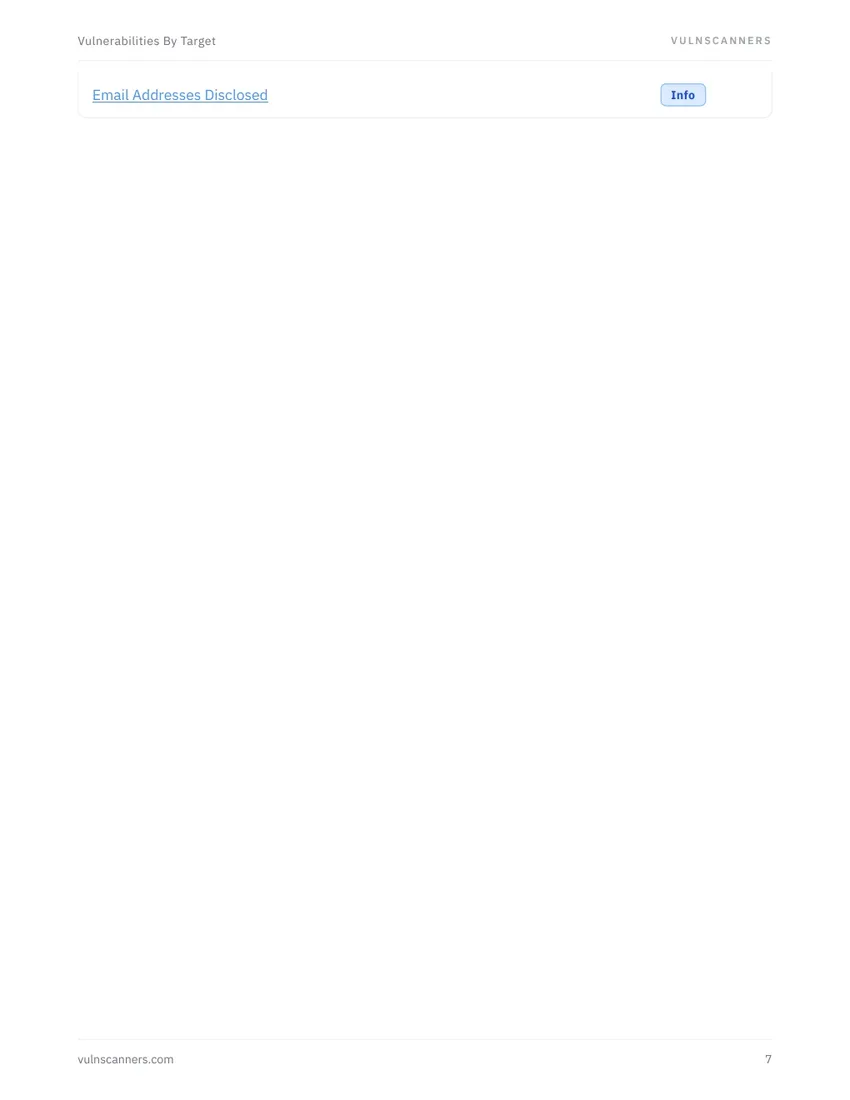
A combined Nmap, Nuclei, testssl.sh & OWASP ZAP assessment — executive summary, severity breakdown, and detailed findings with business impact, remediation, and copy-paste verification steps. Enter your work email and we'll send the full PDF to your inbox.
FAQ
You can — they're excellent open-source tools. The cost isn't running the scan, it's keeping it production-ready: Nuclei ships new templates almost daily, ZAP add-ons and Nmap scripts drift, and client allowlisting needs a stable source IP a laptop or CI runner doesn't have. We run and update all four engines from a fixed origin, keep your scan history, and turn the raw output into a clean, client-ready report — so you get the findings without babysitting the tooling.
You only scan assets you own or have written authorization to test — that responsibility is yours, and it's built into our terms. Scanning targets you don't have permission to test violates those terms and, in most places, the law. The platform is built around authorized testing, not spray-and-pray.
Every finding ships with its evidence and a copy-paste command to verify it yourself, so you can confirm what's real before acting on it or handing it to a client. Nuclei's template-based checks are high-signal by design, and ZAP findings include the request/response context. You decide what's worth reporting.
Results are stored encrypted and are only accessible to your team. You can export to PDF or delete any scan at any time — including raw output.
One scan on one engine — Nmap, Nuclei, OWASP ZAP, or testssl.sh — against an approved target, with its own PDF report. A full four-tool pass on one target is four credits. Packs start at $10 for 10 assessments.
Never. Credits stay on your account until you use them.
Yes — a 7-day no-questions-asked refund on your first purchase. After that we handle issues case-by-case.
Most Nmap scans finish in 1–10 minutes. Nuclei sweeps against a single target typically take 5–15 minutes. OWASP ZAP varies the most — a passive scan and spider can wrap in ~10 minutes; a full active scan against a large app can take up to about 30 minutes. Scans run in the background, so you don't have to keep the console open.
Unified web app. Four scanners. Evidence-backed output your team can triage, fix, and verify.